01 / WORLD → AGENT
Protect the agent from what it reads.
Detect hostile instructions, unsafe skills, malicious packages and suspicious tool output before they influence an agent's next action.
Blackbox-compatible local guard
AI agents can read files, run commands and reach your network. Axiom helps you stay in control of what they do — and what reaches them.
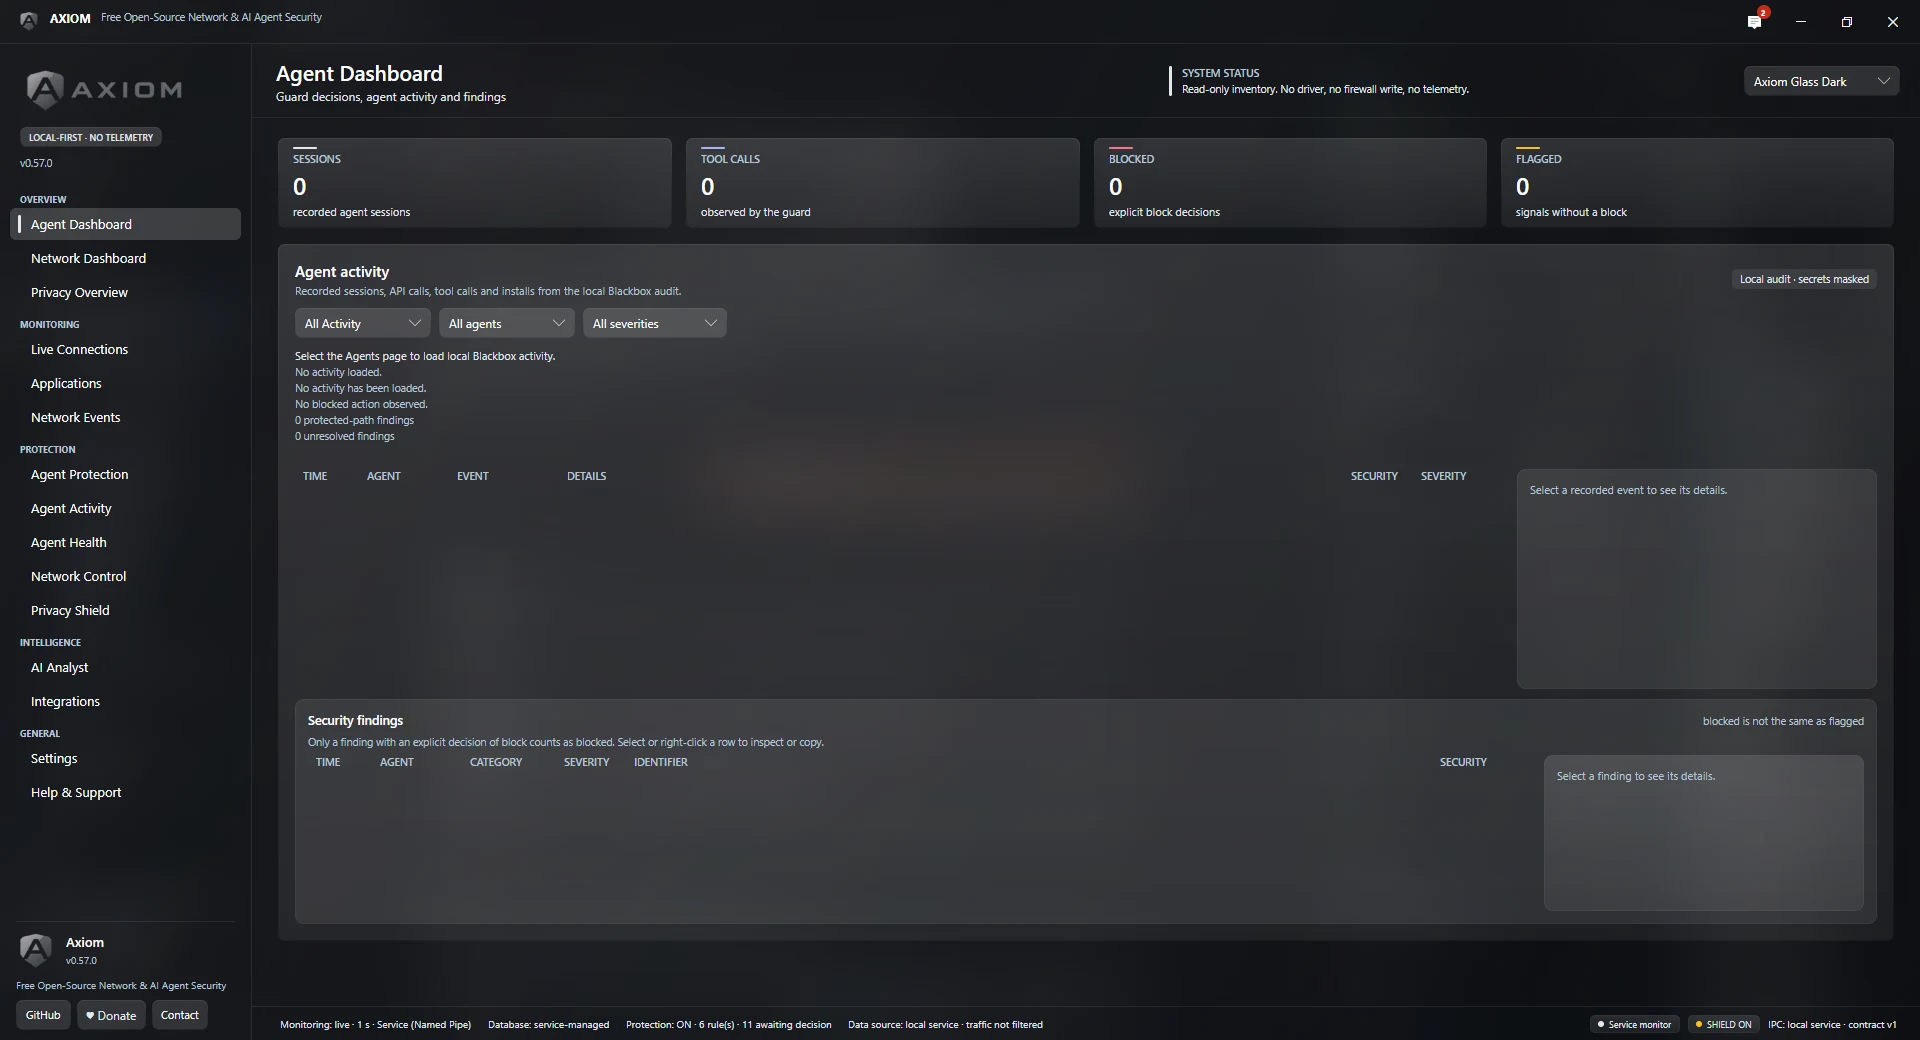
Security for the machine that runs the agent — and for the agent processing untrusted content. Axiom combines local guard decisions with system-level controls where the operating system supports them.
Detect hostile instructions, unsafe skills, malicious packages and suspicious tool output before they influence an agent's next action.
Watch tool calls, sensitive-file access and outbound activity, applying scoped local policy and verified OS controls where available.
Keep visibility into local processes and network connections. Manage Axiom-owned firewall rules and filter unwanted DNS activity using local policy and curated lists.
Illustrative overview — actual protection states are reported individually in Axiom.
A guard verdict is not automatically a proven block. Axiom distinguishes observation, policy decisions, OS read-back and confirmed outcomes.
Agent actions, process context, file access and network events.
Local policy, Blackbox guard signals and verified intelligence.
Apply a supported hook or operating-system boundary.
Show what was attempted, what was blocked and what is unverified.
Existing OS firewall rules and locally available guard policies can keep working offline. After synchronization, cached Blackbox/DKG intelligence remains available as last-known context — without pretending it is a fresh sync.
Axiom can use the Agent Blackbox guard and OriginTrail DKG threat knowledge while helping people contribute higher-quality observations back to the ecosystem.
Provenance-aware threat knowledge
and curated intelligence.
Detection, guard decisions
and approved reporting.
AXIOMLOCAL POLICY & CONTROLObserve. Decide.
Enforce where supported.
Scoped policy, guard decisions
and supported OS controls.
Filtered, sanitized observations.
Shared only with user approval.
Axiom keeps reports local until the user approves them. Candidates are normalized, checked against provenance and excluded sources, sanitized and submitted through the Blackbox reporter.
Community findings do not automatically become firewall blocks. Signed reports are not the same as curator-verified threats.
A single Axiom experience across Windows, macOS and Linux, with operating-system-specific enforcement and transparent capability reporting.
Axiom is an independent open-source project within OpenDKG. The organization develops practical tools around technologies that bring real value to users — and welcomes the people who want to help make them better.
Meet OpenDKG OPEN-SOURCE ORGANIZATION
Built for Windows, macOS and Linux. Distribution links will appear here when the public releases and platform checks are ready.